Classify, Score, Govern & Validate Your Sensitive Data.
ClassifyScoreGovernValidate your sensitive data in one platform.
TagmAiT finds the personal and regulated data hiding in your cloud, databases, documents and SaaS apps. It scores its risk, locks it down with real access control and generates the evidence your regulator asks for.
Whether your data is on AWS, Databricks, BigQuery, Snowflake, Azure, Alibaba, SharePoint, Google Drive, Salesforce or on premises, TagmAiT has you covered.
From Raw Columns to Governed, Scored, Provable Data
No agents to install. No data copied out. TagmAiT reads your catalog, samples values in place and writes tags, policies & evidence back to your platform.
01 - SCAN
See what's sensitive
Point it at a warehouse, lake, bucket, document store or SaaS app. Value based detection finds PII and regulated data, even in oddly named columns or free text.
02 - SCORE
Know where the risk is
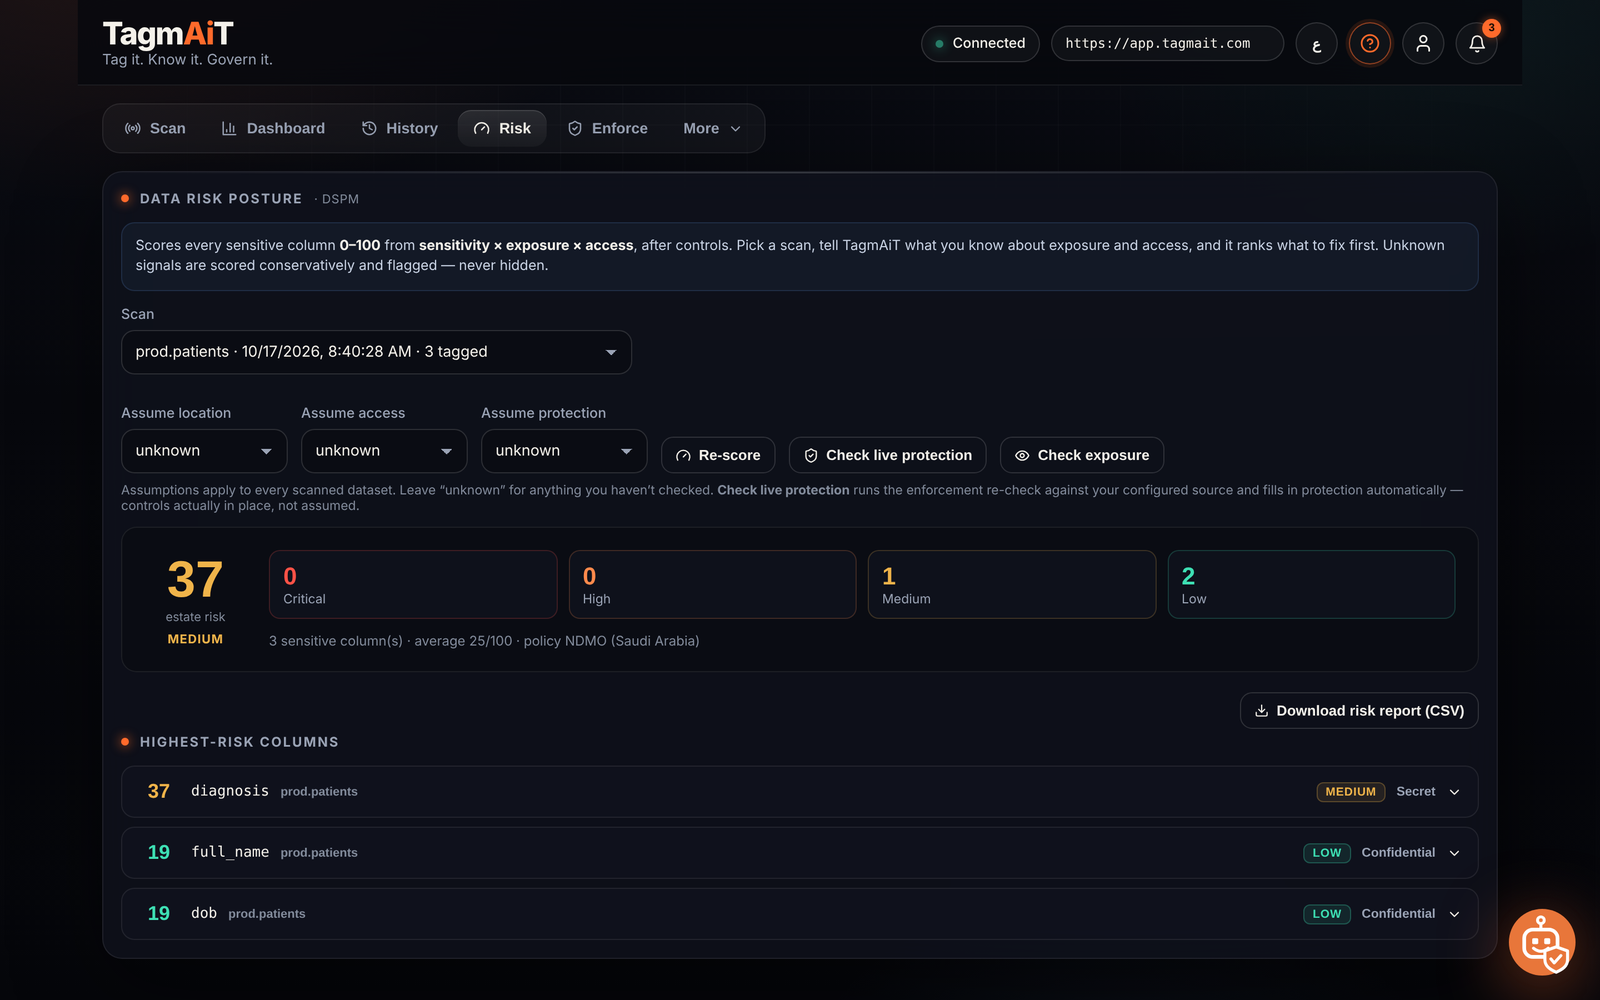
TagmAiT scores every sensitive asset by sensitivity, exposure & access, so you see exactly who can read what, where it's over-shared & which copies are sprawling into dev & backups.
03 - REMEDIATE
Lock it down automatically
Generate masked views or native column security. TagmAiT even lets you Git version policy to auto apply enforcement the moment new sensitive data appears which you can then re-verify on a cadence.
04 - PROVE
Hand the auditor the evidence
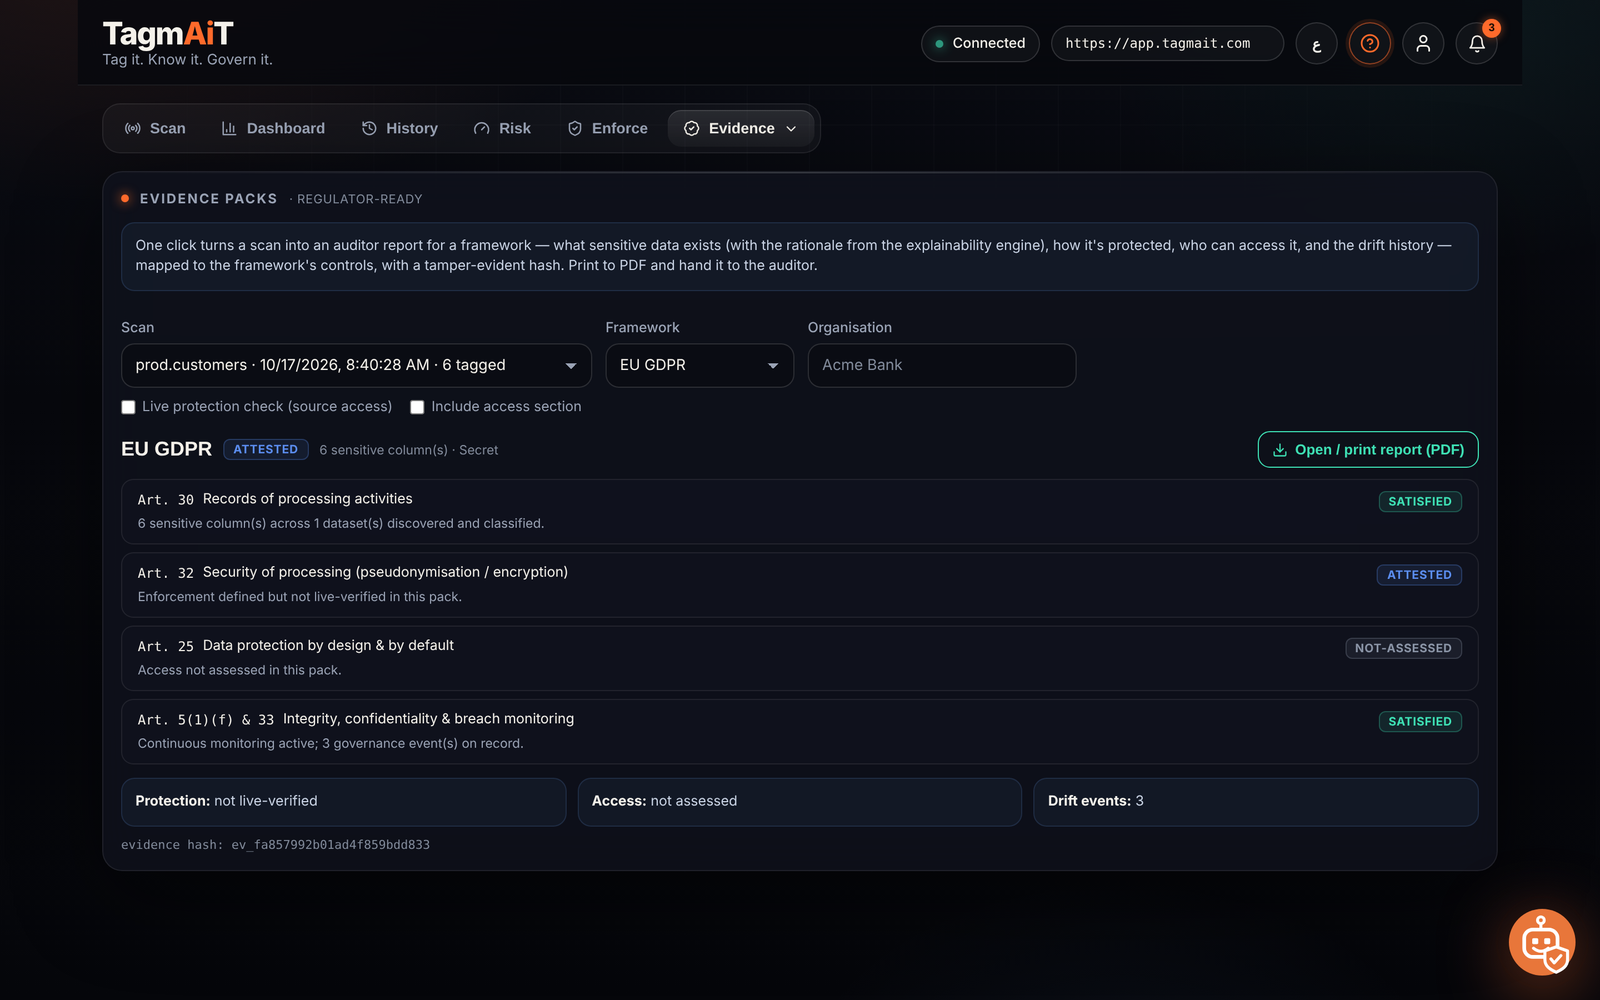
With one click TagmAiT can provide a PDPL, GDPR or PCI evidence pack. Detailing what exists, how it's protected, who can access it, drift history as well as answering "if this is breached, what's exposed and is the 72-hour clock tripped?"
What you get
A complete data security posture platform
Classification is only the start. TagmAiT scores the risk, shows who can read what, guards the data feeding your AI, finds the copies sprawling across your estate and generates the evidence. All from one engine, all in your own tenant.
Value-based detection
Looks at the actual data, not just column names, so it catches an IBAN or a national ID even when the column is called col_7.
Data risk scoring (DSPM)
Every sensitive asset scored by sensitivity, exposure & access with a posture dashboard. Most DSPM tools only tell you about risk, TagmAiT also fixes it because it generates the enforcement.
Real enforcement
Generate masked views or native security: Lake Formation LF-Tags, BigQuery policy tags, MaxCompute Label Security & Unity Catalog governed tags with ABAC column masks & row filters,
Regulator-ready evidence
One click turns a scan into a PDPL, GDPR, PCI, NDMO or CCPA pack. What exists, how it's protected, who can access it, drift history, all mapped to the framework's controls with a tamper-evident hash.
Visual review & tag
Every match comes with confidence and evidence. Confirm, correct or suppress in a click while human judgement stays in the loop.
Bulk estate onboarding
Discover every database in an account and scan them in one pass, so a whole estate gets classified without wiring up each source by hand.
Shadow-copy detection
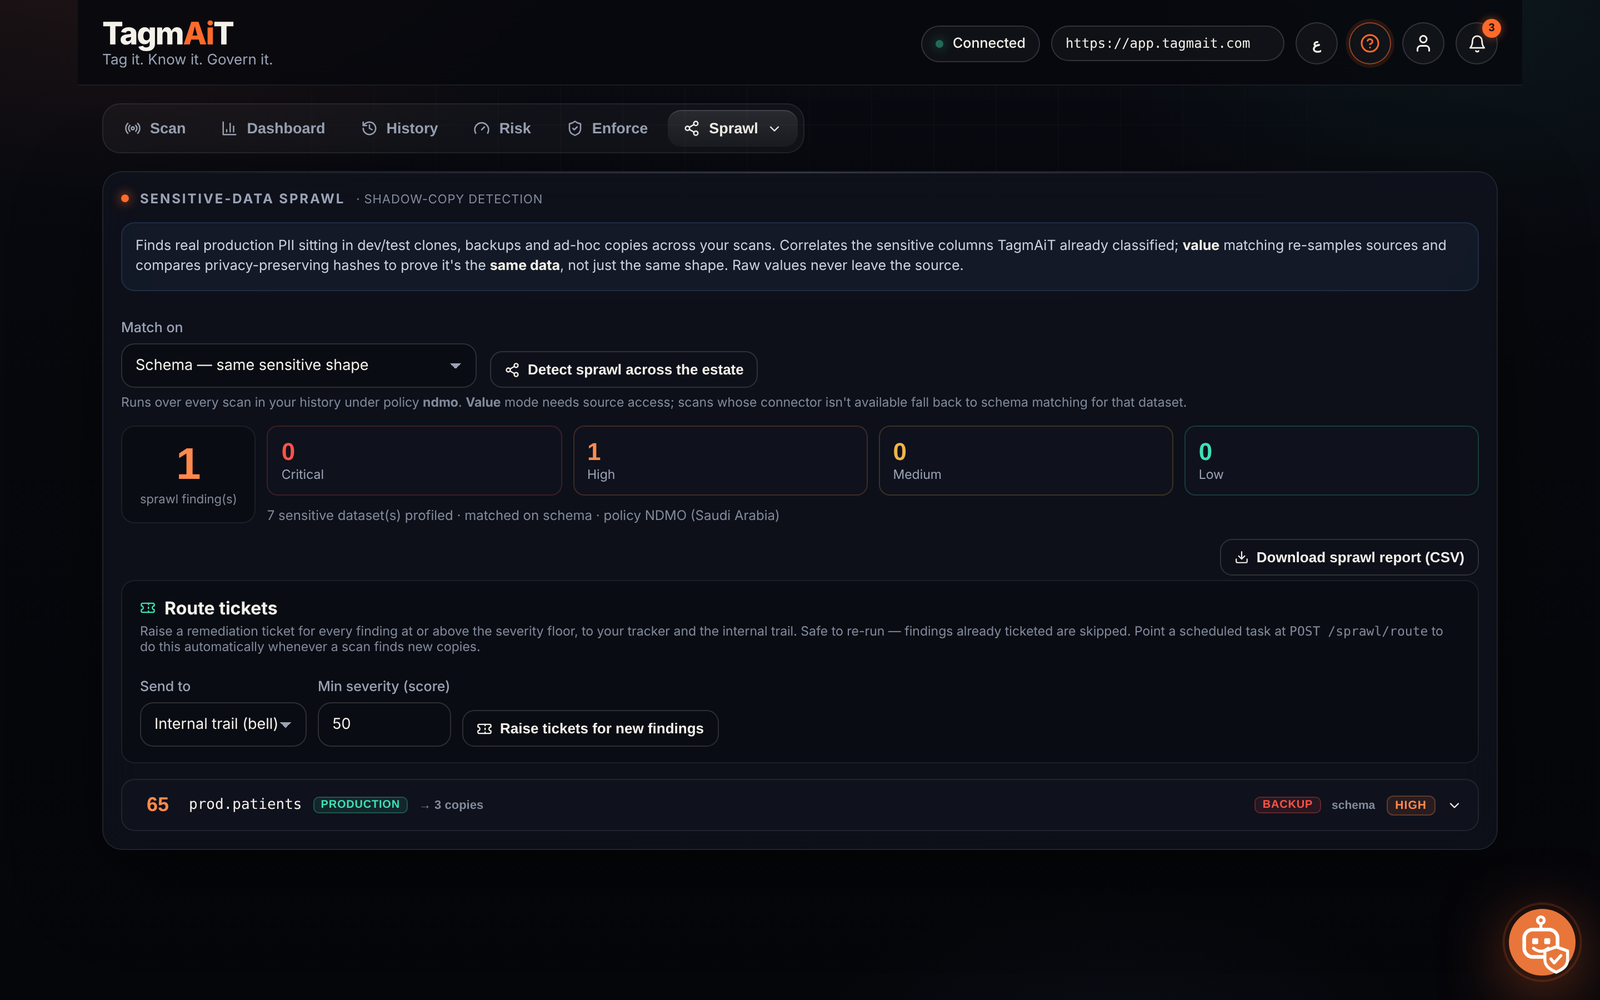
Finds real production PII sitting in dev/test clones, backups and ad-hoc copies. Proven by privacy-safe value fingerprints with one-click remediation and ticket routing.
Deep regional catalogue
130+ validated identifier types: checksum-validated national & tax IDs across the GCC, APAC and EMEA/Africa (Emirates ID, Aadhaar, Singapore NRIC, Australia TFN, China Resident ID and dozens more). Plus GDPR Article 9 special-category and secret detectors the US-centric tools skip.
Documents, repositories & mailboxes
Scan 20+ sources: SharePoint, OneDrive, Box, Drive, Dropbox, Confluence, S3/GCS, Exchange & Gmail mailboxes and more. Across Word, Excel, PDF (scanned via OCR), email and archives, quickly pinpoint findings in document, redact a copy, write native sensitivity labels back and run DSAR / right-to-erasure.
Your whole estate on one screen
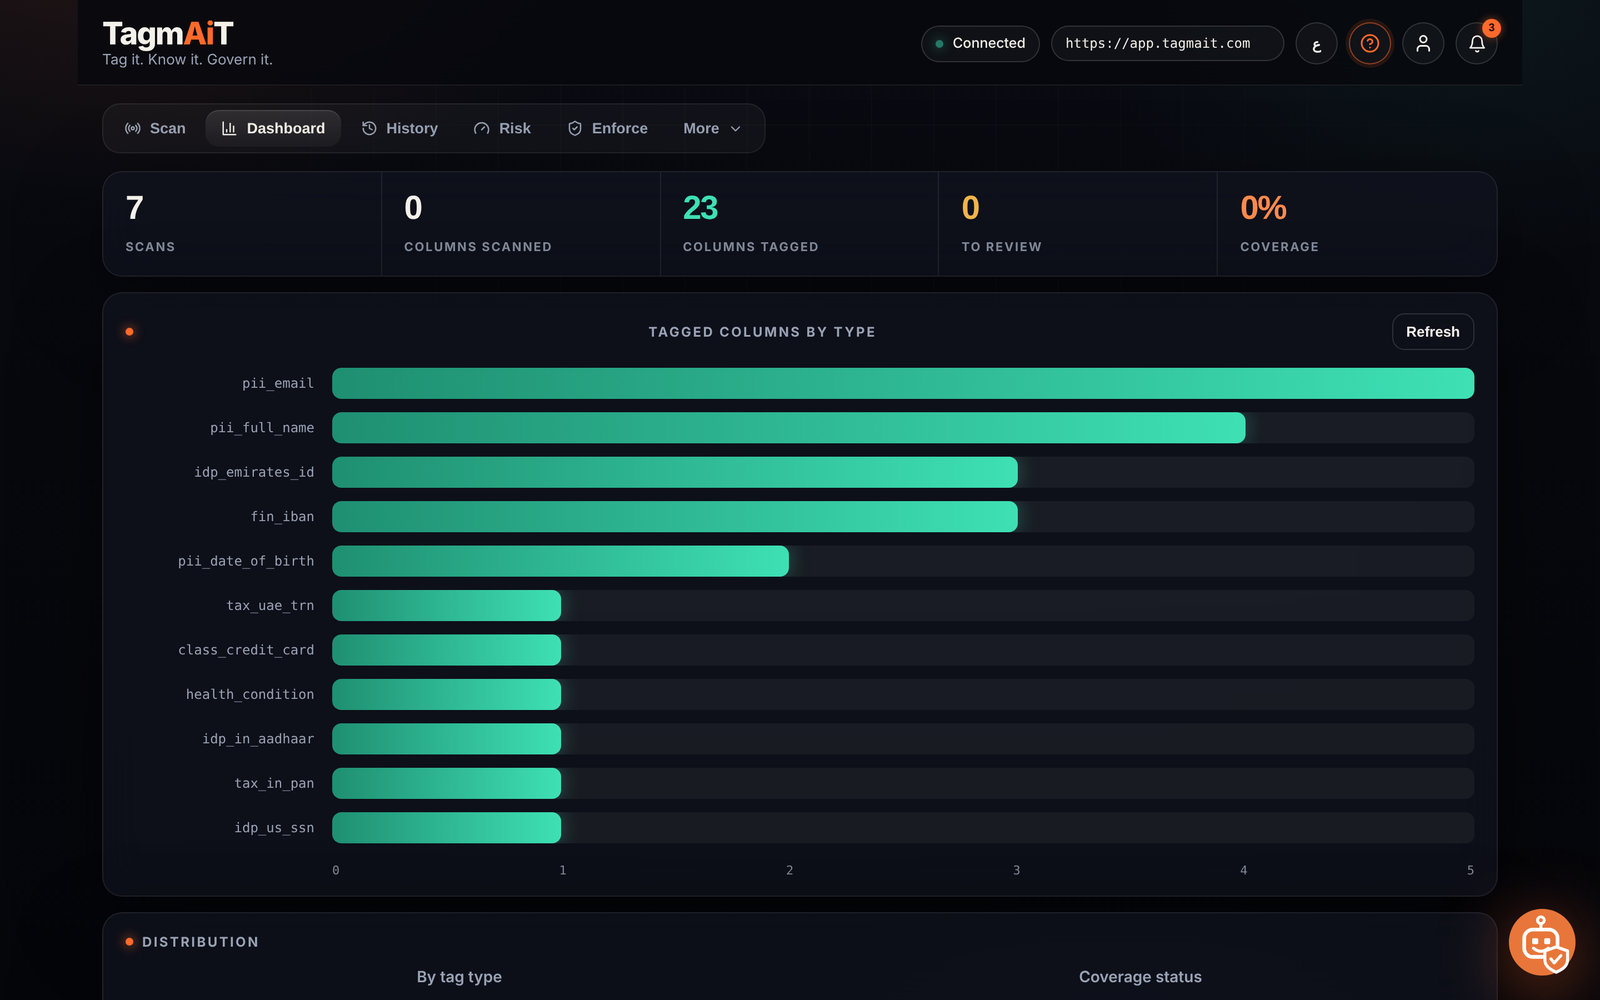
A single command center for the executive view: your estate risk score, what needs attention right now, the most sensitive columns ranked and live PDPL / GDPR / PCI / NDMO compliance readiness. Scattered findings become one decision with no spreadsheet archaeology before the board meeting.
Drift re-verification
Re-check on a schedule that the controls you applied are still there and get alerted the moment a view is dropped or a tag disappears.
AI / RAG guardrails
Redact or block sensitive columns before they reach an LLM pipeline, fine-tuning set or vector database such as pgvector, Pinecone or Weaviate. On Databricks TagmAiT also traces which UC registered models and feature tables are fed by regulated columns. TagmAiT stops Shadow AI leaking PII into embeddings.
Policy-as-code
Define "all PII masked for role X" as a Git-versioned policy. TagmAiT auto applies the enforcement the moment new sensitive data appears. Continuous, idempotent, CI-friendly.
Explainability reports
Per-column evidence and rationale you can export. TagmAiT shows the audit trail that shows why each column was classified the way it was.
Access intelligence
Who can read each sensitive column is resolved to real principals. TagmAiT provides over-permission alerts when data is readable by everyone, by too many or shared org-wide.
Breach blast-radius
If a table or credential is compromised, TagmAiT show you exactly what regulated data was exposed, roughly how many data subjects and whether the PDPL/GDPR 72-hour notification clock is tripped.
An audit trail that survives the audit
Every scan, tag, enforcement and key is recorded and hash-chained to the one before it, so a single altered or deleted entry breaks the chain and shows. Verify integrity in one click and stream it live to Splunk, Microsoft Sentinel or ArcSight - the tamper-evident accountability record your PDPL, GDPR or SOC 2 auditor asks for, built in.
Governance that runs in your pipeline
Mint scoped, revocable API keys and run classification straight from CI/CD without a human login. New sensitive data is caught the moment it ships, not at the next quarterly audit. Every automated call is role-checked, rate-limited and written to the same tamper-evident trail.
Raises the ticket where your team works
The moment a scan finds sensitive data, open a Jira issue or ServiceNow record straight from the findings. Pre-filled with every column, its tag and classification level, severity drawn from the data and a stable fingerprint so re-scans de-duplicate instead of piling up. The work lands in the queue your team already lives in, not a PDF nobody opens.
Syncs to the catalog you already trust
Push every classification into Microsoft Purview, Collibra or Alation, so TagmAiT's findings appear per-column, right where your data stewards already look. One engine classifies once. Your catalog, your SIEM and your ticket queue all stay in step with no parallel source of truth to reconcile.
Coverage
The right control for each platform
TagmAiT does not stop at a tag. Pick a platform and watch it write that platform's own native enforcement, not a lowest common denominator.
One engine. Every platform's own enforcement. No lowest-common-denominator tags.
All-in on Databricks? TagmAiT governs Unity Catalog natively
Most scanners stop at applying a tag. TagmAiT drives the full Unity Catalog governance loop. Defining governed tags and policies, reconciling the ones you already have, propagating them along lineage and proving who can read what and who actually did. It runs as a Databricks App inside your own workspace.
Deployed as a Databricks App via Asset Bundle in your own workspace. Scans execute on your SQL warehouse and write tags, policies and evidence back to Unity Catalog - your data never leaves your tenant.
One classification engine utilising each platform's own governance primitive.
One classification engine. Each platform's own governance primitive. Databricks is the deepest; everywhere else gets the same scoring, sprawl detection and evidence packs.
Bulk-discover every database in the account and scan them in one pass
Native LF-Tag enforcement - masked and filtered access, no bespoke policies
Checksum-validated detection with a deep regional ID catalogue
Feeds the same risk scoring, shadow-copy detection and evidence packs
TagmAiT reads the Glue Data Catalog and samples values in place through Athena - nothing is copied out of your account. Classifications are written back as Lake Formation LF-Tags, so access control is enforced natively at query time.
Column-level security from the taxonomy - no manual policy-tag wiring
Per-source coverage on the dashboard, most-sensitive first
Risk scoring and regulator-ready evidence over your warehouse
Guardrails before data feeds a Vertex or LLM pipeline
Reads INFORMATION_SCHEMA and samples in place across datasets and projects. Tagged columns become BigQuery policy tags, so column-level security is enforced by BigQuery itself.
Native masking policies applied from a single approved plan
Scheduled re-verification with drift alerts when a mask is dropped
Full DSPM scoring - sensitivity × exposure × access
One-click PDPL / GDPR / PCI evidence packs
Connects to your account and warehouse and samples values in place. TagmAiT generates and applies Snowflake masking policies on sensitive columns, then re-checks they are still there.
Surface regulated data in storage nobody is cataloguing
Object-level risk scoring and shadow-copy detection
Pairs with your SQL sources for one estate-wide posture
Evidence and blast-radius across structured and unstructured
Scans Azure Blob containers - CSV, Parquet, JSON and documents - with a connection string or workload identity, classifying object-level sensitivity in place.
Native MaxCompute Label Security for column-level control
APAC-first detection, incl. China Resident ID and more
The same scoring, sprawl and evidence as every other source
Runs in your own region - no data egress
Reads the MaxCompute (ODPS) schema and OSS buckets, with a regional catalogue tuned for APAC identifiers.
Works on-prem or in any cloud, behind your own network
Masked views or column grants generated per role
Re-verification and drift alerts on a schedule
The same classification engine as your warehouses
Connects over JDBC to PostgreSQL and JDBC-compatible databases, reads information_schema and samples in place. Enforcement is a masked view or role-based column grants.
Pinpoint each finding's location in the document - page, line and a masked snippet
Download a redacted copy with every sensitive value blacked out
OCR catches data in scanned contracts and ID photos column tools never see
A per-file risk score and it flows into the same evidence and audit packs
Scans unstructured files with the same checksum-validated detection used on database columns, finding PII buried in free text that column-name tools miss. Handles Word, Excel, PowerPoint, PDF - including scanned/image-only PDFs and photos via OCR - email (.eml/.msg/mbox), RTF/OpenDocument and whole .zip/.tar/.7z archives.
Email mailboxes - Exchange & Gmail - the biggest uncontrolled PII store most tools skip
Write a native sensitivity label back to each file (Microsoft Purview/MIP, Drive) - real enforcement for documents
Flag & restrict over-shared files - public links, org-wide shares - and find shadow copies by fingerprint
DSAR & right-to-erasure: find every document mentioning a data subject, across the estate
Connects to your document repositories, object storage and mailboxes and scans the files and records inside - OAuth or a token at run time, nothing exported. The same engine that reads a database column reads a SharePoint library, a Box folder, an S3 bucket or an Exchange mailbox - then governs them: write-back, over-share, DSAR and dedup.
One classification. Every source's own enforcement. Structured and unstructured.
How we compare
Why not just use the tools you already have?
Cloud native scanners are single-cloud and tuned for global identifiers. The big catalogs cost six figures and label without enforcing. TagmAiT addresses that gap.
One engine. Native enforcement. Regional IDs. Runs in your tenant.
Classify, score risk, surface shadow copies and generate an auditor ready pack all from one shared view your security, data and compliance teams can act upon immediately.
app.tagmait.com/dashboardLive
Coverage0%
shadow copy found in dev
ResidencyMaskingAccess control
Pack ready
Classify, score risk, surface shadow copies and generate an auditor-ready pack. Produced from one shared view your security, data and compliance teams can act on immediately.
A single violation can reach: 5M SAR under Saudi PDPL · up to 5M AED under UAE PDPL · £17.5M or 4% of global turnover under UK GDPR · €20M or 4% under EU GDPR · 50M AUD (or 30% of turnover) under Australia's Privacy Act · or compound per consumer under California CCPA. TagmAiT safeguards you at just a small fraction of the above. Buy direct, or through your cloud marketplace.
Start with a Proof of Value - $6,000
4-6 weeks, one estate, your real data. POV purchase is fully credited to your licence when you buy.
Indicative, annual, ex-VAT. A data source = one database, catalog, warehouse or bucket. Add extra sources for +$3,000 each / year. Start with a $6,000 Proof of Value, fully credited to your licence. Multi-year pricing available; final quote on scoping.
FAQ
Questions teams ask us first
Does my data ever leave my environment?
No. TagmAiT connects to your warehouse, lake or cluster, reads the catalog and samples values to classify them in place, then writes tags and policies back to your platform. The classification runs inside your tenant.
How is this different from my cloud's built-in DLP?
Cloud-native scanners like Purview, Macie and Cloud DLP are tied to one cloud and tuned for global identifiers. TagmAiT works across every major cloud from one place and detects region-specific data - GCC, APAC and EMEA national IDs, IBANs, VAT numbers, all checksum-validated - that those tools routinely miss. It goes further than labelling, too: it scores the risk, shows who can read what, writes each platform's native access control, finds sprawling copies and generates the audit evidence - one engine, discovery to proof.
Can it stop sensitive data leaking into our AI / RAG pipelines?
Yes. The AI/RAG guardrails redact or block sensitive columns before they're embedded into a vector database (pgvector, Pinecone, Weaviate) or written into a fine-tuning set, so "shadow AI" doesn't quietly copy regulated data into your models. The gate is enforced again at the vector store, so blocked fields can't slip through in metadata.
What do we hand the regulator after an incident?
A one-click evidence pack for PDPL, GDPR, PCI, NDMO or CCPA - what sensitive data exists, how it's protected, who can access it and the drift history, mapped to that framework's controls with a tamper-evident hash. And if a table or credential is compromised, the breach blast-radius shows exactly what regulated data was exposed, roughly how many data subjects and whether the 72-hour notification threshold is tripped - with the deadline counted from discovery.
What does deployment involve?
Connect a source from the UI, or run the connector in a notebook - scan, review the matches and apply. No agents sit in your data path. Most teams start with a scoped Proof of Value and are classifying real data within 4-6 weeks.
How does enforcement actually work?
TagmAiT generates a masked view, or writes your platform's native column security - Lake Formation LF-Tags, Unity Catalog governed tags & ABAC, BigQuery policy tags, MaxCompute Label Security, Snowflake masking policies - then re-verifies on a schedule that the control is still in place.
We're a Databricks shop - what do we get beyond tagging?
The full Unity Catalog governance loop. TagmAiT defines governed tags and their policies for you, reconciles the tags already in your catalog and propagates them along system.access.column_lineage so a label follows the data downstream. It pairs who can read each sensitive column with who actually did (from system.access.audit), lists what leaves your tenant through Delta Sharing, traces which UC registered models and feature tables are fed by regulated columns and writes ABAC column masks and row filters. Scans run incrementally on only the tables that changed and the whole thing deploys as a Databricks App in your own workspace.
Can we buy through our cloud marketplace?
Yes. TagmAiT is available as a private offer on the Azure and Google marketplaces, so it goes on your existing cloud bill. You can also licence direct.
Is TagmAiT SOC 2 certified?
SOC 2 Type II is in progress. In the meantime we're glad to walk through our security posture and data-handling details under NDA.
Know where your Sensitive Data is by this time next week.
Witness TagmAiT run against source data like yours. Book a 30-minute walkthrough and see a sample estate classified live.
Thanks - we'll be in touch at the email you gave within one business day.